geschätzte Lesezeit: 6 min

This blog post is about open vs private or closed APIs. For the web service specification, see OpenAPI Specification.

A few months ago I wrote a blog post about how important it is to make dev teams at FAIRTIQ independent and specifically how we leveraged Kafka to address a facet of it. In this blog post I’m looking at the same topic with a broader view: using open APIs to make companies independent while still having them benefit from one another. To illustrate it, I created an app that connects FAIRTIQ and Slack.

You’ve experienced it, the symbiosis

Over the past decade more and more companies have allowed developers to build applications on top of their platform and data. You are probably familiar with the “Sign in with Google” button that provides a 1-click registration to your favourite website using your Google account data, or the “Impress your friends” in your awesome video game’s leaderboard, which would make all your Facebook buddies jealous about your new high score.

A high score screen with a button to share on Facebook. Source: Pinterest

This kind of feature is possible thanks to open APIs. A company makes some data and actions publicly available for any developer to use in their own applications (in contrast to closed or private APIs). Generally, that benefits both parties. In the examples above, Google and Facebook get more accounts or activity on their services, whereas the developers can leverage the platforms to get more visibility or provide simplified user registration.

Open APIs allow platform providers to leverage the creativity of an ever growing developer community to come up with innovative applications that add value to their core business without investing directly in the development of these.

When any developer can use an open API to make cool things within our accounts, they can also do things which are less cool, all the way down to malicious. The data privacy question comes naturally to our mind. It turns out that the rules regarding who can do what and see what are set by the platform provider, i.e. the one providing the open API, holding the data and enabling the predefined actions. In most cases there is an authorisation flow, where the user grants the permission for instance to Acme inc to post on their Facebook feed on their behalf. Once the permission is granted, it remains valid until the user explicitly revoked it.

Open APIs and FAIRTIQ

Whereas FAIRTIQ provides open APIs for the public transport organisations (to connect their pricing systems for instance) it doesn’t provide a user-facing open API as of now. Let’s see how it could look like in a very simple form. An open API can be seen as a set of data to read, events to be notified about and actions to be performed.

FAIRTIQ’s hypothetical simple user-facing open API

One could argue that this is rather limited. However the full power comes when combined with other services or open APIs. Let’s say you want to create an app called “Travel with me buddy”. You could ask the user’s permission to access their FAIRTIQ check-in information and their Facebook friends. When two friends check in at the same time and place, you would send both a notification. As an event organiser, you could promote public transport to join the venue. You’d connect your event app to FAIRTIQ so that participants get credits to spend on-site based on how many kilometers they travelled with FAIRTIQ. Or as a home hacker, you’d make sure your vacuum cleaner robot starts worrying about your floors as soon as you leave your home and check-in.

The possibilities are endless. Some of them are home hacks and fun whereas others can be large scale revenue generating businesses. Given the potential, I want people at FAIRTIQ to start thinking “open API”. It’s a mindset. Something to have in the back of your head anytime regardless whether you are a developer, a sales person or a product designer. In order to make it more tangible and sparkle some ideas, I created the Commuting bot.

Check in with FAIRTIQ, followed by a status change on Slack

The Commuting bot is an app that automatically changes an employee's Slack status to “Commuting” whenever they are checked in with FAIRTIQ and restores it to whatever it was before when they check out. It leveragesSlack’s open API and FAIRTIQ’s inexistant open API (an internal simulation).

For this to work, the Commuting bot must obtain the user’s permission to be notified by FAIRTIQ whenever they check in and out, and from Slack to read and change their status. On the FAIRTIQ side, we do not support this authorisation model yet as we don’t provide an open API, so I hard coded it. On Slack, this is achieved by setting up a Slack App and setting the appropriate scopes.

Commuting bot slack app.

It’s worth noting that the Slack app contains no app logic. It’s only a way to request the appropriate permissions to the Slack user when they will install the Commuting bot. I created a basic web interface that allows FAIRTIQ employees to connect their Slack account to their FAIRTIQ account. After authenticating with FAIRTIQ and pressing “Connect” they are redirected to a page provided by Slack where they authorise the Commuting bot to edit their Slack profile on their behalf.

Commuting bot web interface

Slack’s authorisation page

From now on, the Commuting bot monitors the check in and checkout events on FAIRTIQ and adjusts the user’s Slack status in consequence. Behind the scenes, when the user grants permission to edit their Slack status, the Commuting bot obtains a token that allows it to act on Slack on the user’s behalf (as if it was the user themselves). This authorisation remains until the token is revoked. That can be done by clicking “Disconnect” in the Commuting bot or by uninstalling the Commuting bot app from Slack.

And it scales

Both companies FAIRTIQ and Slack most likely don’t care that much about Michel’s Commuting bot. That said, they also haven’t invested a single penny in it*. They only provided an open API that millions of Michels can use to innovate and/or serve their own business needs. Surely, providing an open API has a cost, however it’s mostly independent from the number of use cases that run on it. Make the open API once, let millions use it.

There are actually operational costs when running an open API, which are dependent on the usage, but they are usually marginal, provided that you have measures in place to prevent abuse (e.g. a developer sending billions of requests). For large scale usage, such APIs can also be monetised.

* Ok, I’m an employee of FAIRTIQ so that wasn’t completely free for us, but assume I wasn’t.

Conclusion

The benefits for both the open API provider and the consumer depend a lot on the use case being developed. Usually it’s a win-win situation: both parties mind their own business and on top they help each other without specifically investing in doing that. The open API provider leverages worldwide innovation for free, while at the same time unlocking new business opportunities for all the others. These new use cases, when successful, generally have a positive direct or indirect impact on the open API provider’s business.

Open doesn’t necessarily mean free. It means it’s not restricted to specific people or companies. An open API can be monetised if it makes sense to do so. Nevertheless, it must be done very carefully as it could easily defeat the purpose if it becomes a barrier to adoption. Freemium models (pay only if you make money with it) can be adequate.

Finally, open APIs are a great way to make systems interoperable. This becomes increasingly important, as systems grow in complexity and size. A big fat system operated by a single company will age much faster than a composition of multiple smaller, interoperable systems, each maintained by another specialised company.

Ah, and the title’s question? Well, now you know…
geschätzte Lesezeit: 4 min

Table of Contents

This article demonstrates how to recursively update specific key in multidimensional array in PHP. 

Multidimensional arrays add alot to the complexity than a linear array. Similarly, updating specific keys in a multidimensional array using an iterative approach is complex and unpredictable. 

So, in this article, we take up the challenge and explore how to update specific key in multidimensional array in PHP. 

The article “How to update key value in array PHP” explores three options for changing keys in a linear array. 

  • A loop approach.
  • The direct indexing approach.
  • Using PHP array_search function.

Out of these three, direct indexing stands out in terms of efficiency. That said, this article will use a mix of these to develop a generic function to handle multidimensional arrays.

Before diving into code examples, let’s first see the multidimensional array.

$students =
[
   "Sam" =>   ["Exam#1" => 87],
   "Brian" => ["Exam#1" => 80],
   "Chris" => ["Exam#1" => 92],
   "Sarah" => ["Exam#1"=> 90]
];

The array $students is a two-dimensional array. The objectives here are to

  • Find the key in multidimensional array.
  • Update specific key in multidimensional array.

Let’s see an example that uses a loop and direct indexing to update the key “Exam#1” to “MidTerm” in all the subarrays. 

Advertisements
<?php
$students =
[
   "Sam" =>   ["Exam#1" => 87],
   "Brian" => ["Exam#1" => 80],
   "Chris" => ["Exam#1" => 92],
   "Sarah" => ["Exam#1"=> 90]
];
function changeName($array, $oldKey, $newKey)
{
    foreach($array as $k => &$v)
    {
        if(array_key_exists($oldKey, $v)) //If key exists in the subarray
        {
            $value = $v[$oldKey];    //Passes the value to a variable using direct indexing.
            $v[$newKey] = $value; //Make a pair with the new key.
            unset($v[$oldKey]); //Unsets the old key and value pair.
        }
    }
    return $array;
}
$students = changeName($students, 'Exam#1', 'MidTerm');
?>

Here’s the breakdown of the function changeName.

Advertisements
  • The loop iterates through the array and $v refers to the subarrays.
  • PHP array_key_exists checks if the key is available a subarray.
  • The block within array_key_exists updates the key and unsets the older one.
  • Finally, the function returns the updated array.

 So, here’s the output of the function for the array above.

Array
(
    [Sam] => Array
        (
            [MidTerm] => 87
        )
    [Brian] => Array
        (
            [MidTerm] => 80
        )
    [Chris] => Array
        (
            [MidTerm] => 92
        )
    [Sarah] => Array
        (
            [MidTerm] => 90
        )
)

Looks cool! But let’s assume the multidimensional array changes to something as follows.

Advertisements
$students =
[
   [
       "Name" => "Sam",
       "Exams" => [
           "Exam#1" => 87
       ]
   ],
   [
    "Name" => "Brian",
    "Exams" => [
        "Exam#1" => 80
    ],
    [
        "Name" => "Chris",
        "Exams" => [
            "Exam#1" => 92
        ]
    ],
    [
        "Name" => "Sarah",
        "Exams" => [
            "Exam#1" => 90
        ]
    ],
],
];

It seems gibberish but worse than that is the function doesn’t support this structure. It will instantly throw an error. In simpler terms, it is not generic enough. So, what’s the way out then?

The way out is writing a generic function using recursion. So, up next we’ll see how to update specific key in multidimensional array using recursion.

Recursive algorithms adapt to arrays regardless of their dimensions and that’s why they are super flexible and robust. The following example uses a recursive function to update specific key in multidimensional array in PHP.

function changeName(&$array, $oldKey, $newKey)
{
    foreach($array as $k => &$v)
    {
        if(gettype($v) == 'array')
        {
            if(array_key_exists($oldKey, $v)) //If key exists in the subarray
            {
                $value = $v[$oldKey];    //Passes the value to a variable using direct indexing.
                $v[$newKey] = $value; //Make a pair with the new key.
                unset($v[$oldKey]); //Unsets the old key and value pair.
            }
            else
            {
                changeName($v, $oldKey, $newKey); //Go a level deep to find the key.
            }
        }
    }
}

The changeName function has been modified into a recursive function. The core logic of updating the key looks the same. The recursive calls happen if the function doesn’t find the key in a subarray. 

Advertisements

So, it will go as many levels down as possible just to find and update a specific key. Also, note that we are not returning from the function because it takes the array by reference thus making in place changes.

Here’s the output.

Array
(
    [0] => Array
        (
            [Name] => Sam
            [Exams] => Array
                (
                    [MidTerm] => 87
                )
        )
    [1] => Array
        (
            [Name] => Brian
            [Exams] => Array
                (
                    [MidTerm] => 80
                )
            [0] => Array
                (
                    [Name] => Chris
                    [Exams] => Array
                        (
                            [MidTerm] => 92
                        )
                )
            [1] => Array
                (
                    [Name] => Sarah
                    [Exams] => Array
                        (
                            [MidTerm] => 90
                        )
                )
        )
)

Voila! We’ve made a generic function to update specific key in a multidimensional array in PHP.

The article overviews the challenges in working with a multidimensional array and then explores an example that is non-generic but successfully updates a specific key. Then, the article moves to a generic recursive function that updates a specific key in a multidimensional array of any depth.

Hopefully, you’ve liked this article. Learn more about PHP at FuelingPHP. 

We have many fun articles related to PHP. You can explore these to learn more about PHP.

geschätzte Lesezeit: 5 min

So, you’ve got your brand new pristine machine and you’re keen to kick off a new Python project. You know you want to use packages that others have written and focus only on the code you need to write. So you head off to github, find your favourite package and turn to the readme to get it installed - it seems dead simple just a ‘pip install’ away. Nothing could possibly go wrong. Right?

Did you spot what the problem is? It’s easy to miss since many packages don’t point out best practices or alternatives to pip in their READMEs. In fact looking at some of the most popular Python projects we can see this problem there - requests, Pillow, and Scrapy. The problem is most readmes completely skip mentioning virtual environments and often lead new devs (and those from other languages) down a poor path. This isn’t a documentation problem, but one deep within Python itself.

The Problems with pip

If you’ve ever experienced this, let me break down whats wrong. When you add a package in this way is you’ll be installing and possibly upgrading the global version of Python packages present on your system. When you come to install another package for your next project you may well end up with conflicting dependencies. Lets say you use the same package again, but theres been a new release with some additional features. When you upgrade your global Python to use it, you now need to ensure every project you’ve done now works with it. That’s annoying and unlikely to happen, what you’ll be left with is a broken build.

Global Installation

Lets use an example of using requests the http request library - First lets go ahead and install it.

pip install requests

This installs latest version into our system Python, but also doesn’t capture which version anywhere, the only notice we’ve got of what was installed is what is output in the terminal. Your global python packages will be installed somewhere other than your project folder, so you can’t easily locate them.

Manual Capture

If we want to capture what was installed, we need to remember to do it ourselves. We can see the version of packages and anything else it’s installed with pip freeze:

pip freeze
...
certifi=-2022.12.7
charset-normalizer=-3.0.1
idna==3.4
requests=-2.28.2
urllib3-1.26.14

This gives us everything that’s been installed along with requests, crucially all it’s dependencies too. Typically to capture dependencies that have been installed in this way, you’d direct freezes output to a requirements.txt file. Capturing what we’ve installed is paramount if we want to produce a deterministic build and sharing it to other locations than a local machine.

pip freeze > requirements.txt

The problem with this approach is it’s simply a text file, so doesn’t allow us to have types of dependencies, I couldn’t install black to format my code as a development dependency for instance, it gets lumped with everything else.

You might expect if I were to pip uninstall requests that I get back to a clean system, right? Wrong - when do so, I uninstall requests, but none of its dependencies. We can see what’s happened with a pip freeze again.

pip freeze
...
certifi=-2022.12.7
charset-normalizer=-3.0.1
idna==3.4
requests=-2.28.2
urllib3-1.26.14

Instead, I need to manually remember to uninstall using a requirements.txt that I’d captured to.

pip uninstall -r requirements.txt

So it’s simple to manage dependencies with pip, but the problem is remembering all these steps is cumbersome and could be simpler. If you’re a new Python developer, it’s highly unlikely you may be familiar with doing some of these things (or as a developer from another language may assume they’re done for you) and quickly get your system into a horrible mess.

Differences to npm, the Node.js Installer

Let’s contrast this with how you might install packages with another language, like Node.js. In this scenario I’m going to install node-fetch, used for making http requests. I’m immediately directed by the readme to install using npm, which is something that comes down as part of Node:

npm install node-fetch

Once we do this, we have a whole load of things in the folder we just installed into.

drwxr-xr-x  5 ian staff 160B 9 Feb 15:17 .
drwxr-xr-x  3 ian staff 96B  9 Feb 13:48 ..
drwxr-xr-x  9 ian staff 288B 9 Feb 15:17 node_modules
-rw-r--r--  1 ian staff 5.0K 9 Feb 15:17 package-lock.json
-rw-r--r--  1 ian staff 55B  9 Feb 15:17 package.json

We have all our dependencies in a single place, a package.json and package-lock.json indicating all the dependencies and there dependencies together. Crucially we have everything to reproduce what we’ve just installed all through using a npm install along with the json files.

Also, if we npm uninstall node-fetch we actually uninstall everything (including the packages dependencies) along with removing our json files and node_modules directory since nothing is installed anymore. A much better experience in my opinion and what you’d expect to happen.

The Alternatives

There’s no shortage of package management alternatives available for Python that are built for working with virtual environments. Which is part of the problem unfortunately.

  • venv + pip - The one built straight into Python’s standard library but requires you to remember each of the above steps to capture to a file.
  • pipenv - Will automatically create and manage a virtualenv and adds and removes dependencies to a Pipfile
  • Poetry - Good for creating your own packages, uses a pyproject.toml. Typically faster at resolving dependencies.
  • PDM (Python Development Master) which allows you to use packages but without a virtual environment.

How someone is meant to pick between these as a new developer is a mystery. I’ve mostly used Pipenv, but like Poetry for publishing my own stuff. I have a playlist of tutorials on each of the above as videos on YouTube.

Now there are some packages which do things really well. Flask for instance, has a really good set of instructions where it says to use a virtual environment for installing stuff and gives examples of doing so with venv. But most of the time the first suggestion is using pip alone, and I’m not sure that that is the correct default for guiding new developers.

NB. I’m in the process of writing an ebook on virtual environments, subscribe to my newsletter if you’re interested in hearing about it when it launches

geschätzte Lesezeit: 5 min
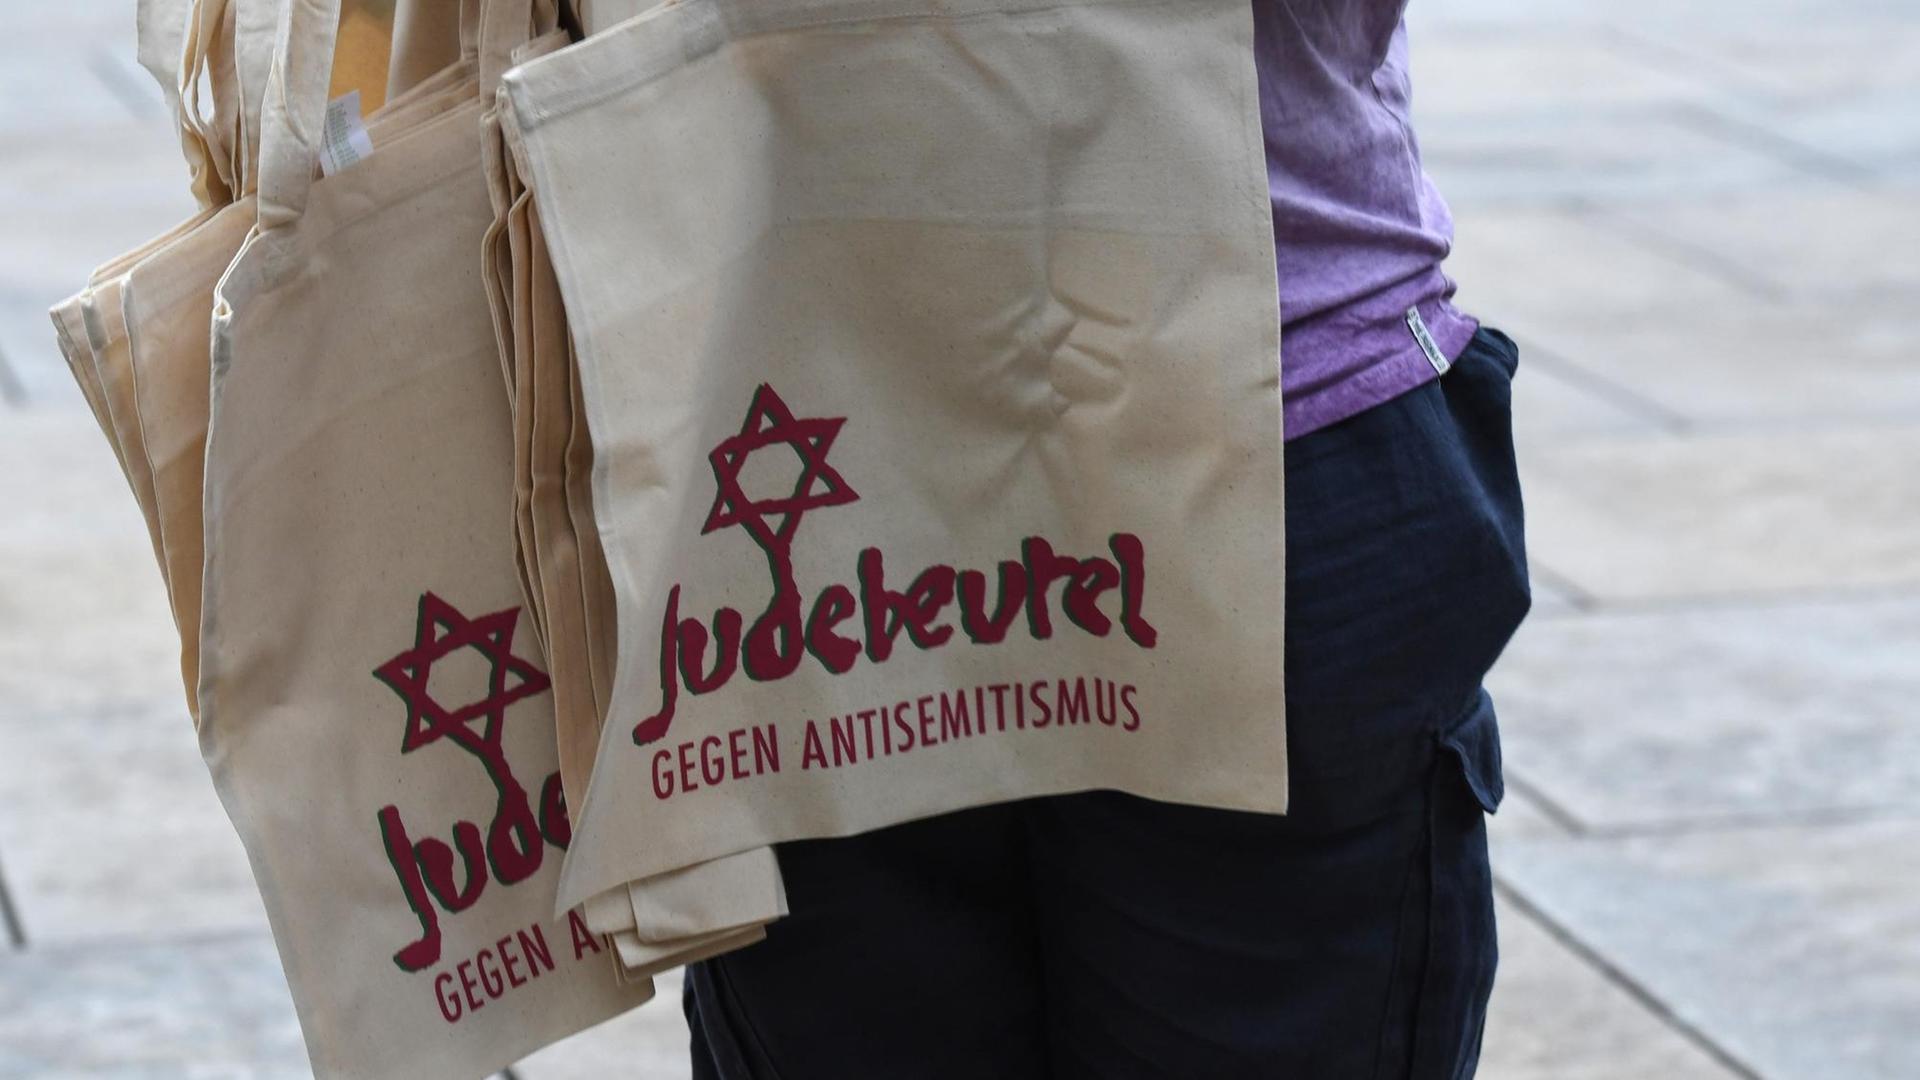
Eine Mann verteilt Einkaufsbeutel mit Davidstern und der Aufschrift: Judebeutel-Gegen Antisemitismus beim Kippa-Tag in Freiburg und der Demonstration gegen Antisemitismus, antisemitische Anfeindungen und Ausgrenzung.
Das Judentum ist ein lebendiger Teil der deutschen Kultur (imago images/Winfried Rothermel)

Kölns Oberbürgermeisterin Henriette Reker twittert. Vor einigen Monaten bezeichnete sie eine Demonstration gegen die Corona-Schutzmaßnahmen als – Zitat - "verschwörungstheoretische und rechtsextreme Mischpoke". Die Frage ist, wer sich danach angegriffen fühlen konnte – allein die Verschwörungsgläubigen oder Jüdinnen und Juden? Das Wort Mischpoke bedeutete im Jiddischen, das vor 100 Jahren noch 10 Millionen Menschen weltweit gesprochen hatten, einfach Familie - "mischpoche". Ganz wertneutral. Weder positiv, noch negativ. Eingedeutscht bekommt es einen düsteren Beiklang, eine Anrüchigkeit, wie eine verschworene Gemeinschaft. Der Journalist Ronen Steinke hat über offen und verdeckt judenfeindliche Wörter und Redewendungen ein Buch geschrieben. Mischpoke kommt darin auch vor:

"Es ist also ein Bedeutungswandel. Wenn man heute von Mischpoke spricht im Deutschen, hat es immer etwas Sinistres, Dubioses, entweder ein korrupter Zusammenhang oder irgendwie eine dunkle Seilschaft. Und dieser Bedeutungswandel ist nur dadurch zu erklären, dass ein gewisses Bild von Jüdinnen und Juden abgefärbt hat auf dieses Wort. Dieser Bedeutungswandel ist etwas, was antisemitisch ist. Deswegen von dem Wort Mischpoke in der Verwendung als irgendwie Negativ-Wort sollte man Abstand nehmen, um nicht dieses antisemitische Bild, dieses Stereotyp zu nähren und zu affirmieren."

7-armiger Leuchter, 1700 Jahre jüdisches Leben in Deutschland

"Geschacher" und "Mauschelei"

Ein anderes Beispiel ist das Wort Schachern. Im Buch schreibt Ronen Steinke:

"Geschacher um Ministerposten, so liest man manchmal. Gemeint ist übles, feilschendes Geschäftemachen. Es kommt vom Jiddischen sachern. Sachern bedeutet im Jiddischen ganz einfach Handel treiben, ohne jeden abwertenden Unterton. Abwertend wird es erst im deutschen Gebrauch als Lehnwort. Nicht der lexikalische Inhalt, sondern allein die jiddische Herkunft sorgt für eine negative Deutung dieses ansonsten wertneutralen Wortes. Die deutsche Sprache macht daraus 'handeln wie ein Jude'."

Und das Ressentiment gegenüber jüdischen Händlern beinhaltete so etwas wie "unlauterer, profitsüchtiger Handel". Je mehr man von diesem Bedeutungswandel erfährt, umso gruseliger wird einem bei der Lektüre. Viele Prägungen stammen noch aus der Zeit vor dem 19. Jahrhundert, wo das Wort Antijudaismus noch nicht erfunden war, aber in der Sprache durchaus anwesend ist. Bei dem Wort Mauscheln beispielsweise erschließt sich der Zusammenhang nicht sofort.

"Das Wort Mauscheln kommt ja heute häufig vor in den Medien: Mauschelei bei der Banken-Fusion oder Mauschelei im Gemeinderat fehlt in keiner Lokalzeitung als Schlagzeile. Das kommt historisch daher, dass der jüdische Vorname Moses oder Mosche - oder Mauschel im deutschen Sprachraum -, der hergenommen wurde als pars pro toto, Name für alle Juden, so ähnlich wie Ali auch in rassistischer Absicht für Türken verwendet wird."

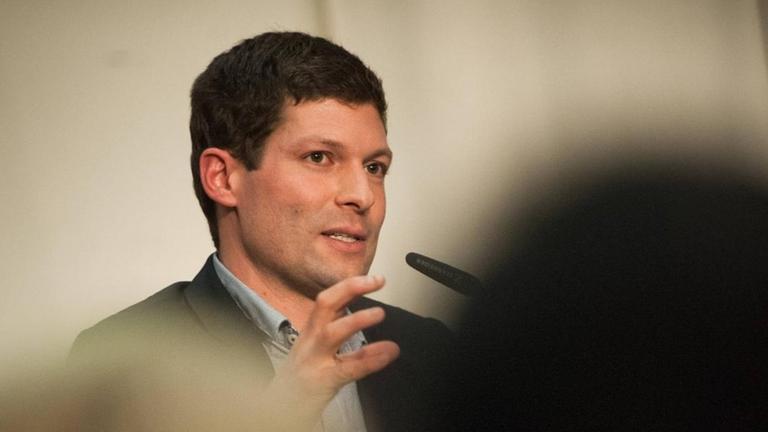
Autor Ronen Steinke bei einer Diskussionsveranstaltung
Ronen Steinke will ein Bewusstsein für Ressentiments in unserer Sprache schaffen (imago/Uwe Steinert)

Der Mauschel, das war also der Jude. Und das Verb mauscheln sollte ausdrücken, dass jemand wie ein Jude redet. Und zwar negativ. Nichts anderes bedeutet dieses Wort bis heute. Abgeleitet von einem Spottnamen für Juden.

"Man mag es vielleicht mit der Intention verwenden, die vollkommen unschuldig ist, dass man ausdrücken möchte, hier werden irgendwie korrupte Dinge besprochen, hinter vorgehaltener Hand im Gemeinderat oder wie auch immer. Aber man greift damit ein altes antisemitisches Klischee auf und verbreitet es weiter."

"Diese Sprechweise ist toxisch"

Ronen Steinke geht es nicht darum, Wörter zu verbieten. Es geht ihm um Aufklärung. Natürlich kann es nicht jeder wissen, wovon sich die verschiedenen jüdischen Begriffe ableiten. Manche seien ja auch ganz charmant: "Meschugge" zum Beispiel für "nicht ganz bei Verstand sein" oder "verrückt werden". Oder "Masel tov" für "Glückwunsch". Aber würde man heute noch von einem "Halbjuden" sprechen, einem Begriff aus der Rassenlehre der Nationalsozialisten. Oder von einem "Judenfriedhof"? Klarer wird das Vorgehen, wenn man es auf andere Religionen anwendet.

"Würde man denn von einem Katholikenfriedhof sprechen? Würde jemand von einem Katholenfriedhof sprechen? Das würde dann doch sofort aufstoßen als eine seltsame, ein bisschen respektlose Formulierung. Der Judenfriedhof ist genau dasselbe. Kein jüdischer Mensch würde selber so von dem Friedhof für seine Großeltern sprechen. Menschen, die von Juden nichts halten, sprechen so. Diese Sprechweise, die in der NS-Zeit ganz populär gemacht worden ist, Judenfriedhof, Judenschule, Judenmusik, Judenliteratur, diese Sprechweise, das ist natürlich toxisch."

Mosaisch? Gut gemeint, aber nicht gut

Die Ausgrenzung von Juden in der deutschen Geschichte ist bekannt. Juden wurden in früheren Jahrhunderten herkömmliche Berufe verboten, sie waren auf den Handel, auch mit Geld, festgelegt. Wenn es Missernten gab, wurden sie als angeblich Schuldige ausgemacht. Ein klares Feindbild. Aber es gab auch gut gemeinte Versuche, die Ausgrenzung von Juden aufzubrechen, ihnen auf Augenhöhe zu begegnen. Es wurden Synonyme gesucht für das arg belastete Adjektiv "jüdisch". "Mosaisch" ist so ein Versuch. Leider geht dieser Begriff für die jüdische Religion völlig am Selbstverständnis der Juden vorbei.

"'Mosaisch' zum Beispiel ist im 19. Jahrhundert geprägt worden, bewusst als neues, unbelastetes, irgendwie leichtherzigeres Wort anstelle von 'jüdisch'. 'Jüdisch' war damals schon sehr belastet, zu toxisch, einfach als Schimpfwort zu oft verwendet worden. Die Intention bei 'mosaisch' ist eigentlich eine gute gewesen. Man wollte sozusagen betonen, dass das Judentum ähnlich wie das Christentum auf einer Stufe steht. Und man hat, so wie das Christentum seinen Namen von seinem Religionsstifter Christus her bezieht, hat man gesagt: Na, dann nimmt man halt den Religionsstifter des Judentums, also Moses, den aus jüdischer Sicht letzten Propheten und bezeichnet dann die Religion in Anlehnung daran."

Antijudaismus - Alttestamentlich contra alttestamentarisch
Der Begriff "alttestamentarisch" wird oft unreflektiert gebraucht, wenn das Alte Testament gemeint ist. Dabei plädieren Theologen schon lange dafür, stattdessen "alttestamentlich" zu verwenden.

Das Problem daran ist, dass es natürlich eine christliche Sichtweise ist. Juden begreifen sich nicht als diejenigen, die Moses als Gottes Sohn oder Religionsstifter verehren, sondern sie sehen etwas anderes im Zentrum ihres Glaubens.

"Und ähnlich wie Muslime auch mit Mohammedaner nicht respektvoll bezeichnet sind. Das ist der Versuch, aus dezidiert christlicher Sicht andere Religionen in ein Schema zu pressen. Und das beinhaltet ja auch ein bisschen die Annahme, es gäbe nichts Schöneres und keine größere Ehre für eine andere Religion, als wenn man sie dem christlichen sozusagen Normalmaß angleichen würde. So ist es nicht. Aus jüdischer oder aus muslimischer Sicht: Nö."

Das Judentum ist Teil unserer Kultur

Wenn sich Ronen Steinke etwas wünschen könnte, dann wäre es, dass Jüdinnen und Juden nicht nur als Opfer und Betroffene mörderischer Gewalt wahrgenommen werden. Das Judentum kann in Deutschland immerhin auf 1700 Jahre Präsenz zurückblicken.

"Noch viel zu selten bequemt sich die Mehrheitsgesellschaft, auch mal die Augen zu öffnen für die vielen, vielen Beiträge jüdischer Menschen zur deutschen Kultur. Es gibt länger deutsches jüdisches Leben als es christliches Leben gibt in Deutschland. Und dementsprechend lang und vielfältig sind die Beiträge zu allem, was wir als deutsche Kultur betrachten. Das immer zu reduzieren auf Holocaust und auf Schtetl und auf Ghettos, das wird überhaupt nicht dem Judentum gerecht. Es ist auch Teil des Problems, dass Juden heute diskriminiert werden."

Ronen Steinke: "Antisemitismus in der Sprache"
Duden Verlag, 2020, 64 Seiten, 8,30 Euro

geschätzte Lesezeit: 6 min
A password manager for NGOs and Foundations

Non-profit organisations handle sensitive information on a daily basis, from donor information to project details. Protecting this sensitive information is a critical part of operations. Having the right password manager in place can help NGOs keep data secure and manageable, which allows your organisation to focus on it’s mission.

Passbolt has a mission of its own — to make password management easy to use, affordable and, most importantly, secure. Nobody, especially an NGO, should have to compromise on security or cooperation. Feel empowered to protect your data by using the right tools for the job.

NGOs vs. Password Security: Winning Combination

“Having a centrally managed and secure password manager system can take the pressure off of an IT team, meaning that major vulnerabilities can be avoided and infosecurity threats will decrease.”
— Cliodhna Kirk, IT Team Lead at Greenpeace

When it comes to cybersecurity and password management, NGOs face some unique challenges. To start, organisations need to securely share passwords with coworkers, sometimes volunteers, and maybe even stakeholders. With multiple accounts to manage, things can quickly get overwhelming. And that’s not even mentioning accessing controls or password audits.

Regular audits of passwords and accounts can be time consuming when performed manually. Without a centralised password management system, there’s no good way to keep track of all your passwords. Organisations with multiple accounts and users might struggle with providing access or monitoring who can view sensitive information.

An NGOs guide for choosing the right password manager

Finding the right tool for your non-profit organisation can be a lot of work, especially if you don’t know what to look for or where to start. There are many password management tools on the market and not all of them might meet the values of your organisation.

The first thing to consider, of course, is security. When choosing a secure solution for your NGO, make sure the password manager uses advanced encryption techniques and has a strong security track record. Look for further security enhancements like 2FA and a customizable password generator. And try to find a platform that doesn’t have a single point of failure.

It’s also important to find a password manager that’s easy for all of your team members to use and navigate. There should be a support team, forum, and documentation that can help if you get caught up in any part of use. There’s no replacement for good customer support.

“One of the main challenges that we faced whilst adopting a password manager was changing the culture around password management: people need to change how they work with and store their passwords. Similar to any IT tooling implementation, what stood out as being important was having clear guidance, communication on the ‘why this is needed’ and training was required in order to get as many people to engage with the tool. Educating users is a fundamental part to mitigating challenges as it’s important for users to understand why they can’t simply store their passwords in an excel file in plain text.”
— Cliodhna Kirk, IT Team Lead at Greenpeace

Not every team member uses the same computers or phones so finding a solution that works for everyone is important. It should work seamlessly across different devices, browsers, and operating systems. A solution limited by the technology your team uses can really hamper the collaboration and access abilities within your organisation.

Choosing a password management system that offers multi-user access is crucial for an NGO with a team that needs access to certain accounts. Access to sensitive information such as donor details, financial records, and confidential communications needs to be stored in a system that’s secure but easily accessible to those who need it. Multi-user access lets more than one person access credentials. Without it, your organisation might have trouble working together safely.

Find one with audit logs and reporting for access. Some password managers provide alerts, set expirations, and keep a log of users who have accessed any given item. Auditing and reporting provides an extra layer of accountability and can help NGOs identify any suspicious activity or attempted breaches.

You’ll also need to consider the cost of the password manager. Security is paramount, but finding a solution that fits within your organisation’s budget is also a big deal. Look for a provider that has flexible pricing plans and discounts for NGOs.

When your organisation is choosing a password manager, the NGOs mission and values should align with the company’s. Choosing a company that aligns, ensures that your organisation is protecting its sensitive information while maintaining integrity, working towards your vision, and keeping a clear identity. A tool can often become an extension of your organisation, having one you trust and align with is crucial.

Implementing A Password Manager

Detailing the steps to implement a password manager at an NGO

Start by defining the scope of your project. Work out exactly what your organisation is trying to achieve with a password manager. Once you’ve identified this, decide what features you need to make it happen. Then find a solution that meets your needs. To make this process easier, you may need to set up a team. A group of tech-savvy, security-conscious people from your organisation. This team can help research solutions, implement the tool, and train the rest of the organisation to use it.

Then it’s important to identify any risks associated. You don’t want your password management tool to become the Achilles’ heel of your organisation’s cybersecurity. Make sure you identify any potential risks and develop a plan to mitigate them. It’s also important to make sure everyone on the team knows what they’re supposed to be doing. Assign roles and responsibilities to keep things aligned and help everyone understand their tasks.

Once you’ve made a decision, set a timeline. Give your team a realistic deadline for implementing a password manager. Make sure everyone is aware of it, so there are no surprises when you’re setting out. Keeping everyone in your organisation informed about what’s going will make the process easier. Tell you employees, volunteers, and stakeholders; they’ll probably be happy to hear what’s being done to protect their sensitive data.

Now you might feel ready to roll out the password manager. But, you should always test it first — after all, you don’t want to be the organisation that accidentally leaks all your donor information because you forgot to test your password manager. Now that you’ve done a run-through, you’re finally ready, but is your team?

It’s time to train your users on how to use the solution effectively and securely. Have some documentation ready or refer to the tool’s documentation. Well-educated users are your best line of defence against cyber attacks. Of course, you can monitor the use of the password manager and identify any issues that need improvement.

Take a look at how the rollout of the new password manager went, review it and see if there are any areas that need improvement. Make notes of the process and don’t forget to refine it as needed. You’ll never know when you’ll need to roll out another tool.

Mission Accomplished

Secure Your NGOs data

It shouldn’t be a challenge to keep your organisation’s data secure. Implementing a password manager can make it easier. For organisations in need of a customisable password manager that puts security and collaboration at the forefront, look no further than Passbolt. It’s a low-cost, open source solution. Get started today with a free trial or contact us about the non-profit discount.